
Architecture & System Design
Advanced engineering for high-trust environments. Specialised AI, HPC, and multi-vendor infrastructure design certified to meet stringent security classifications.


Systems designed to protect the mission. Before a secure system can be deployed, it must be meticulously engineered to withstand modern cyber threat levels while delivering high-performance computing capabilities.
Touchpoint provides comprehensive lifecycle system engineering—from initial concept through to deployment and accreditation. We specialise in complex, multi-vendor infrastructure design tailored specifically for classified government, defence, and enterprise networks operating up to TOP SECRET environments.
Capabilities
System Design Challenges We Solve
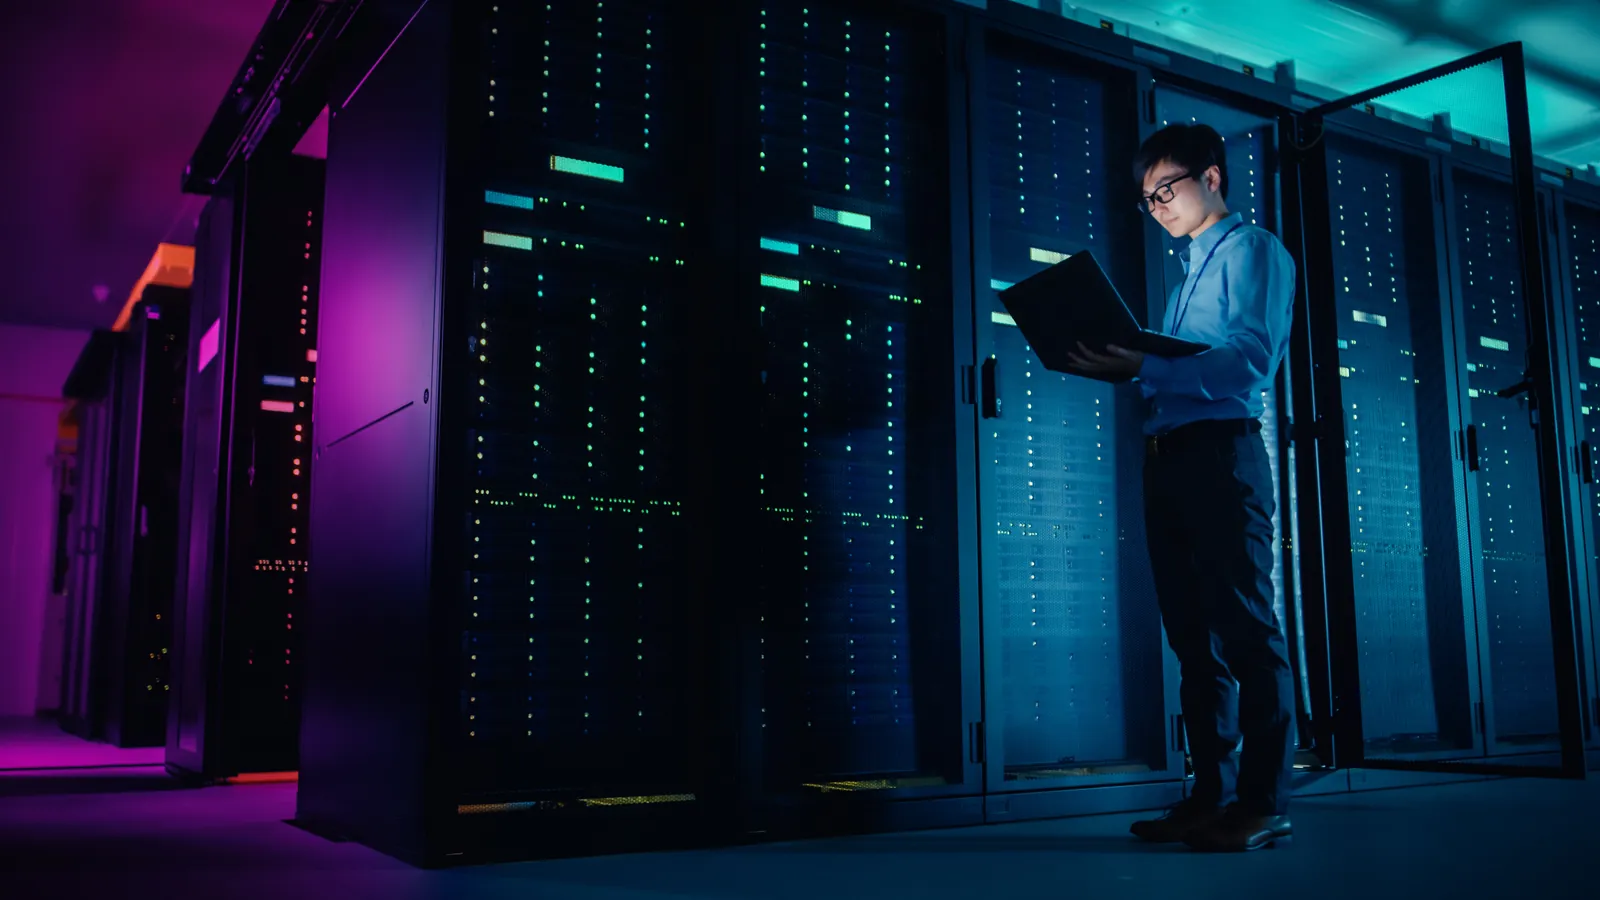
Specialised AI & HPC System Design
Engineering high-performance computing (HPC) arrays and artificial intelligence (AI) infrastructure within highly restricted, classified environments. We balance computational power with security isolation boundaries.
Multi-Vendor Platform Architecture
Bypassing single-vendor lock-in by integrating tier-1 hardware ecosystems (Dell, HPE, NetApp, Cisco, Juniper) into unified, resilient network and storage systems.
ISM Aligned Control Mapping
Translating quarterly updated Information Security Manual (ISM) guidelines directly into the physical and virtual system architecture from day one, eliminating costly retrospective remediation.
Concept-to-Deployment Engineering
Providing end-to-end technical leadership. Our engineering team translates raw operational intent into complete Bills of Materials (BOMs), network topology maps, and deployment blueprints.
Value Propositions
Why organisations choose Touchpoint

Clear Direction Before Investment
We help organisations understand what needs to be designed, why it matters, and how each architectural choice supports the broader operating environment before major commitments are made.

Architecture Built Around the Mission
Every design decision is shaped by operational context, security expectations, performance needs, and long-term sustainment—so the architecture supports how the organisation actually needs to work.

Confidence Across Complex Technology Choices
We bring structure to multi-vendor, multi-platform environments, helping stakeholders compare options, reduce ambiguity, and align on a practical path forward.

Security Considered from the Start
Security, compliance, and accreditation requirements are considered early in the design process, helping organisations make decisions that stand up to scrutiny later.

Specialists Who Translate Complexity
Our team turns technical constraints, competing priorities, and stakeholder requirements into design artefacts that are clear, practical, and usable by delivery teams.

Lifecycle Thinking from Day One
We design with the full technology lifecycle in mind—from deployment readiness through to sustainment, refresh, and future change—so the architecture remains relevant beyond the initial build.
Approach
How we work with you
Discovery & Risk Analysis
We analyse your current infrastructure, constraints, risks, and classification requirements—giving you a clear picture of what must change to support your long-term security goals.
Architect & Design
We translate operational complexity into a secure, scalable architecture—complete with patterns, multi-vendor models, and design artefacts that provide absolute clarity.
Validate & Assure
We test engineering assumptions, model architectural risks, and ensure the proposed infrastructure satisfies performance and compliance parameters before any hardware is procured.
Document & Enable
We produce the final deployment blueprints, full Bills of Materials (BOMs), and compliance pathways your delivery teams need to execute with certainty in the real world.
Partnered with industry leaders to deliver confidence in critical ICT environments






Featured
Newsroom


Ready to strengthen your ICT environment?
Services
Explore Related Services
Learn More
Frequently Asked Questions
How does Touchpoint integrate complex multi-vendor hardware ecosystems into a secure system design?
Our solutions architects hold deep technical integration expertise across all leading tier-1 enterprise brands, including Dell, HPE, NetApp, Cisco, and Juniper. We design cohesive, interoperable technical environments where storage arrays, compute nodes, and network switches communicate seamlessly. By hardening inter-device communication protocols, we eliminate single-vendor lock-in while ensuring the architecture introduces no configuration vulnerabilities or single points of failure.
Can Touchpoint design high-performance computing (HPC) arrays and AI infrastructure for classified networks?
Yes. Touchpoint engineers specialized High-Performance Computing (HPC) clusters and Artificial Intelligence (AI) infrastructure tailored specifically for highly restricted environments up to TOP SECRET classifications. Our system designs strike a precise, dual-purpose balance: maximising high-velocity computational throughput and massive data processing power while enforcing absolute physical and logical security isolation boundaries.
What is the step-by-step collaborative framework for an Architecture & System Design engagement?
We fast-track system readiness and translate operational intent into stable architecture through a structured four-step framework:
Discovery & Analysis: We audit your current systems, constraints, risks, and performance requirements to define clear long-term technical goals.
Architect & Design: We build secure, scalable structural models and design patterns that give clear, unshakeable direction to all stakeholders.
Validate & Assure: We model operational risk, test architectural assumptions, and verify performance metrics before any physical assets are sourced.
Document & Enable: We deliver the complete blueprints, deployment pathways, and configuration rules your delivery teams need to execute with absolute certainty.
At what point in the lifecycle engineering process does Touchpoint incorporate the ASD Information Security Manual (ISM) controls?
We build compliance directly into the initial concept phase of the design process. By mapping the quarterly updated controls of the Australian Signals Directorate (ASD) Information Security Manual (ISM) straight onto our physical and virtual architectural schematics, we eliminate the need for costly, disruptive post-build engineering remediation. This proactive control mapping guarantees a streamlined, predictable pathway to formal system accreditation for federal government security classifications.
What engineering artifacts and documentation are delivered at the conclusion of the system design phase?
We deliver a complete, deployment-ready engineering design package engineered to pass formal security assessor review. The documentation pack includes itemised Bills of Materials (BOMs) with verified hardware provenance, detailed network topology maps, logical/physical separation schematics, firmware interoperability matrixes, and explicit compliance evidence maps aligned to your target security framework.